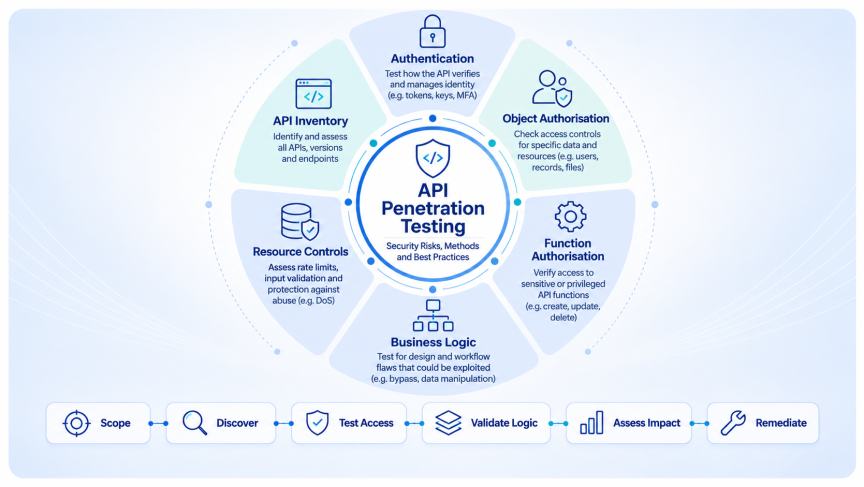
What Is API Penetration Testing? Security Risks, Methods and Best Practices
Application Programming Interfaces, or APIs, allow applications, platforms and services to exchange information and perform actions. They are central to modern digital environments. Mobile applications use APIs to communicate with backend systems, cloud services expose APIs for automation, and organisations increasingly connect internal systems, suppliers and customers through API-driven services. This connectivity also creates security […]
- Penetration Testing
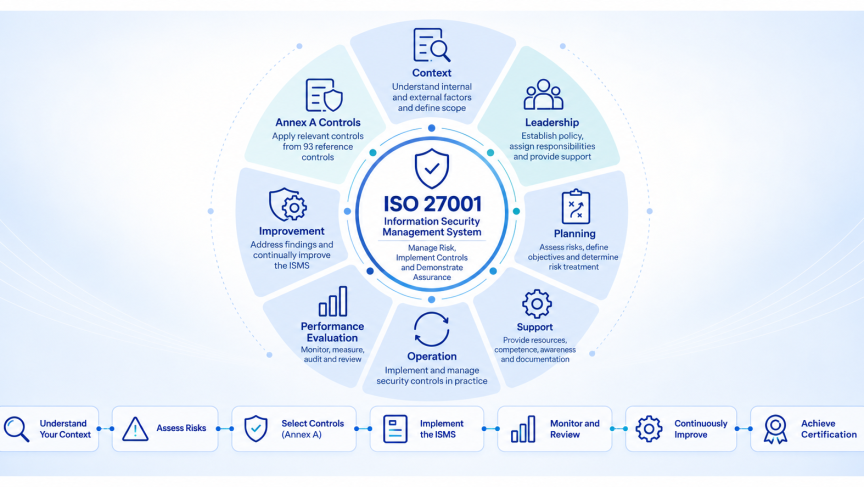
ISO 27001: What It Is, Requirements and Certification
Organisations are expected to protect increasing volumes of information across cloud services, applications, networks, suppliers and employees. Implementing individual security controls is important, but organisations also need a structured way to manage information security risk and demonstrate that their approach is consistent and repeatable. ISO/IEC 27001, commonly referred to as ISO 27001, is an international […]
- Security Assurance
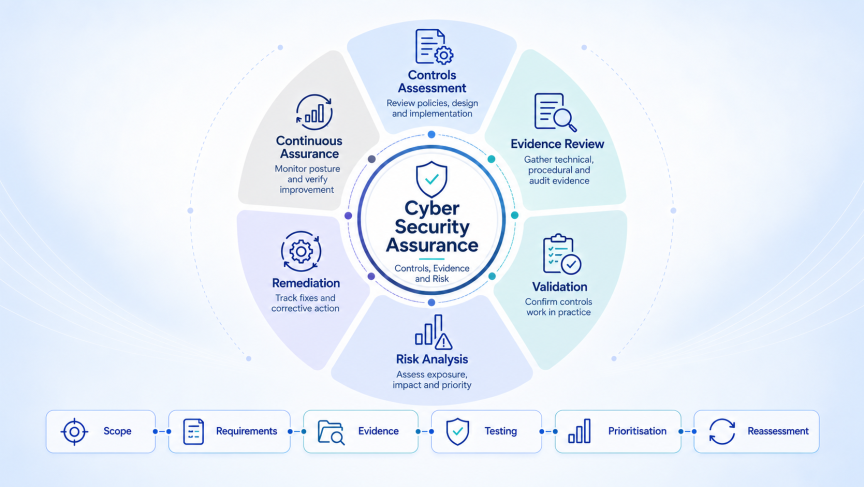
What Is Cyber Security Assurance? Controls, Evidence and Risk
Organisations invest in security controls, policies, testing and technology to reduce cyber risk. The challenge is proving whether those measures are actually working. A firewall may be configured. Multi-factor authentication may be enabled. A penetration test may have been completed. Policies may exist. But none of these activities, viewed individually, necessarily shows how effectively an […]
- Security Assurance
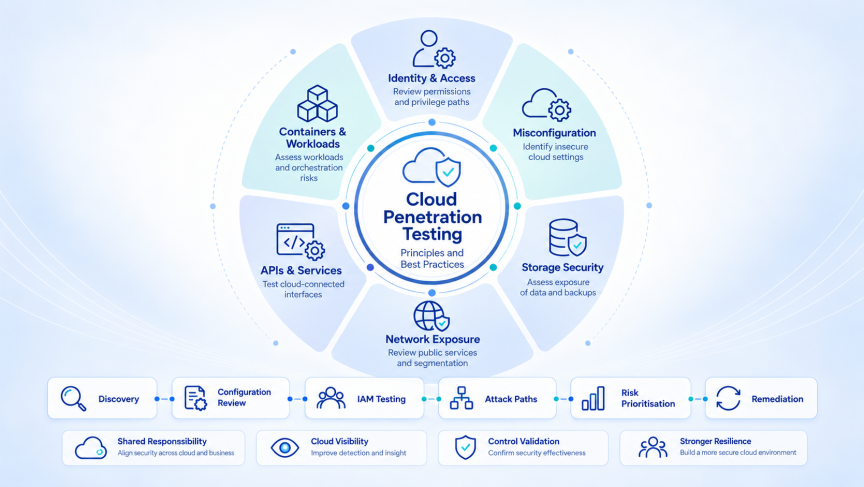
Cloud Penetration Testing: Principles and Best Practices
Cloud infrastructure has become central to how organisations deploy applications, store information and deliver digital services. Platforms such as AWS, Microsoft Azure and Google Cloud allow resources to be created quickly and scaled as business requirements change. That flexibility also changes the security landscape. Cloud environments depend heavily on identity, permissions, configuration and interconnected services. […]
- Penetration Testing
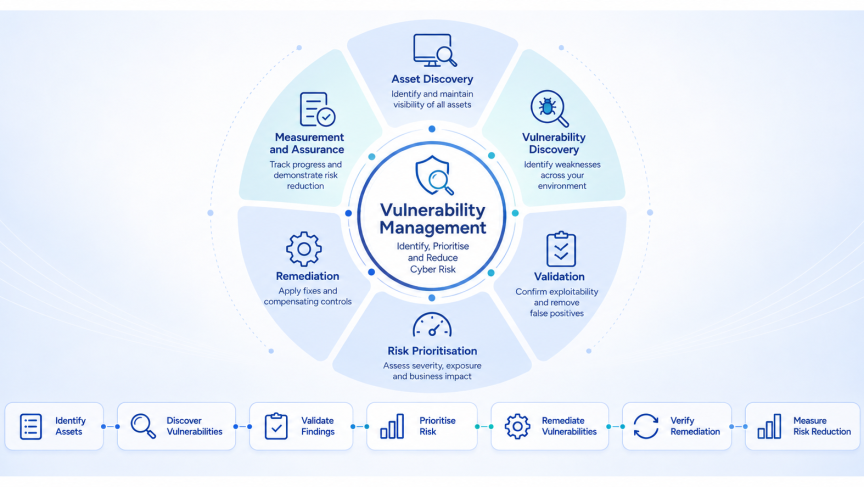
What Is Vulnerability Management? Prioritising and Reducing Cyber Risk
Organisations regularly introduce new applications, cloud services, devices and infrastructure into their environments. At the same time, vulnerabilities continue to emerge in technology that is already in use. The challenge is therefore not simply finding vulnerabilities. Most organisations can generate lists of weaknesses through automated scanning. The more important challenge is understanding which vulnerabilities create […]
- Security Assurance
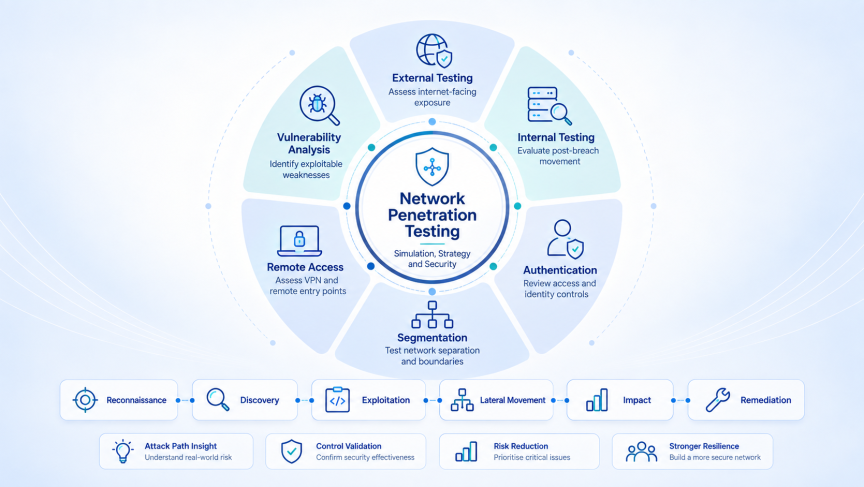
What Is Network Penetration Testing? Simulation, Strategy and Security
Modern organisations depend on increasingly complex networks to connect employees, devices, cloud environments, applications and critical business systems. Firewalls, routers, virtual private networks, remote-access services, servers and identity platforms all form part of this infrastructure. If weaknesses exist within these systems, attackers may be able to gain unauthorised access, increase privileges, move between networks or […]
- Penetration Testing
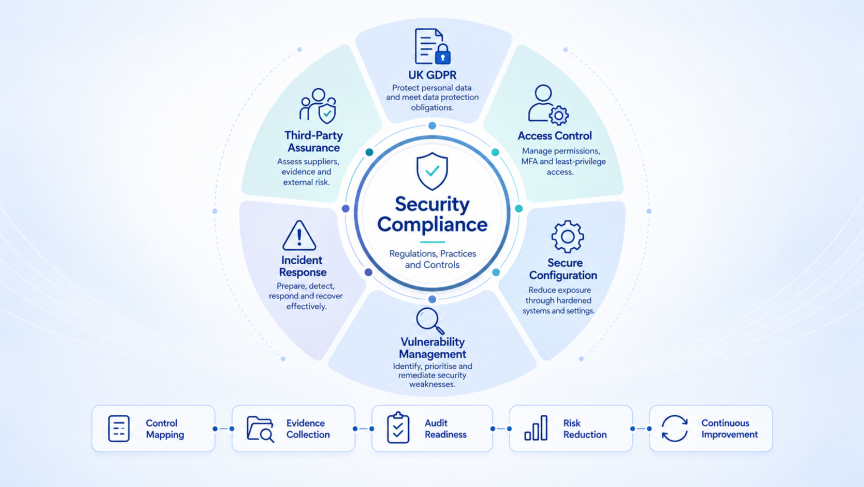
Security Compliance: Regulations, Practices and Controls
Organisations are expected to protect increasingly complex environments containing sensitive data, cloud services, connected systems, employees, customers and third-party suppliers. At the same time, they may need to demonstrate that their security practices meet legal obligations, industry standards, contractual requirements and internal policies. Security Compliance is the process of establishing, maintaining and demonstrating the controls […]
- Compliance
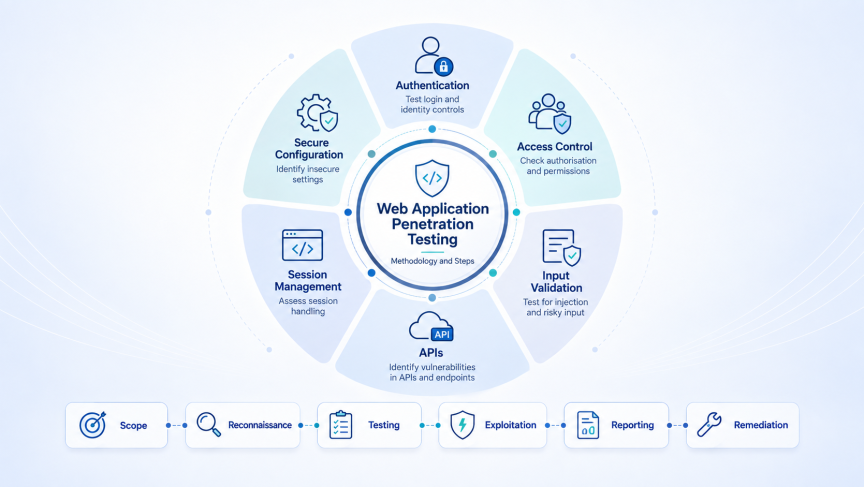
What Is Web Application Penetration Testing? Methodology and Steps
Web applications are central to how organisations deliver services, communicate with customers, process information and support internal operations. Customer portals, e-commerce platforms, cloud-based applications, online payment systems and business software can all expose valuable information and functionality to the internet. As applications become more complex, the number of potential weaknesses can also increase. Authentication systems, […]
- Penetration Testing
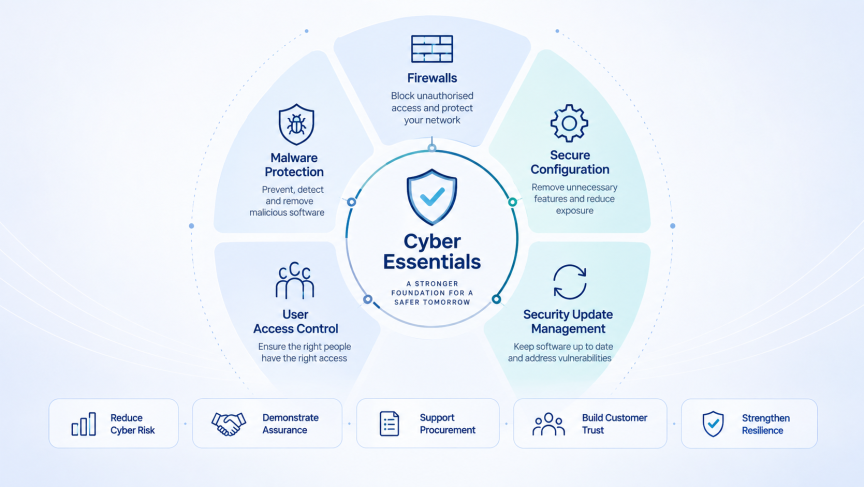
Cyber Essentials: What It Is, Requirements and Certification
Cyber attacks do not always rely on sophisticated techniques. Many incidents begin with common weaknesses such as unsupported software, poor access controls, insecure configurations, exposed services, or insufficient protection against malware. Cyber Essentials is a UK Government-backed cyber security certification scheme designed to help organisations address these fundamental risks. It establishes a baseline of technical […]
- Security Assurance
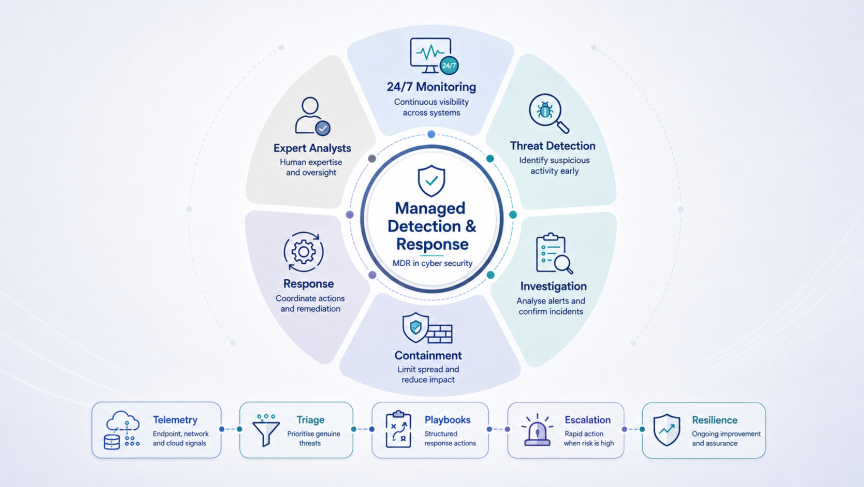
Managed Detection and Response in Cyber Security
Cyberattacks can develop quickly and often occur outside normal working hours. Organisations may have security tools capable of generating alerts, but lack the time, specialist expertise, or internal resources required to investigate every warning and respond effectively. Managed Detection and Response, commonly abbreviated to MDR, addresses this problem by combining security technology with human analysis, […]
- Security Assurance